Building an AI Vishing Solution in 7 Days
 A quick and dirty guide on how to rapidly deploy a fully autonomous conversational AI agent for voice-based social engineering
Read more…
A quick and dirty guide on how to rapidly deploy a fully autonomous conversational AI agent for voice-based social engineering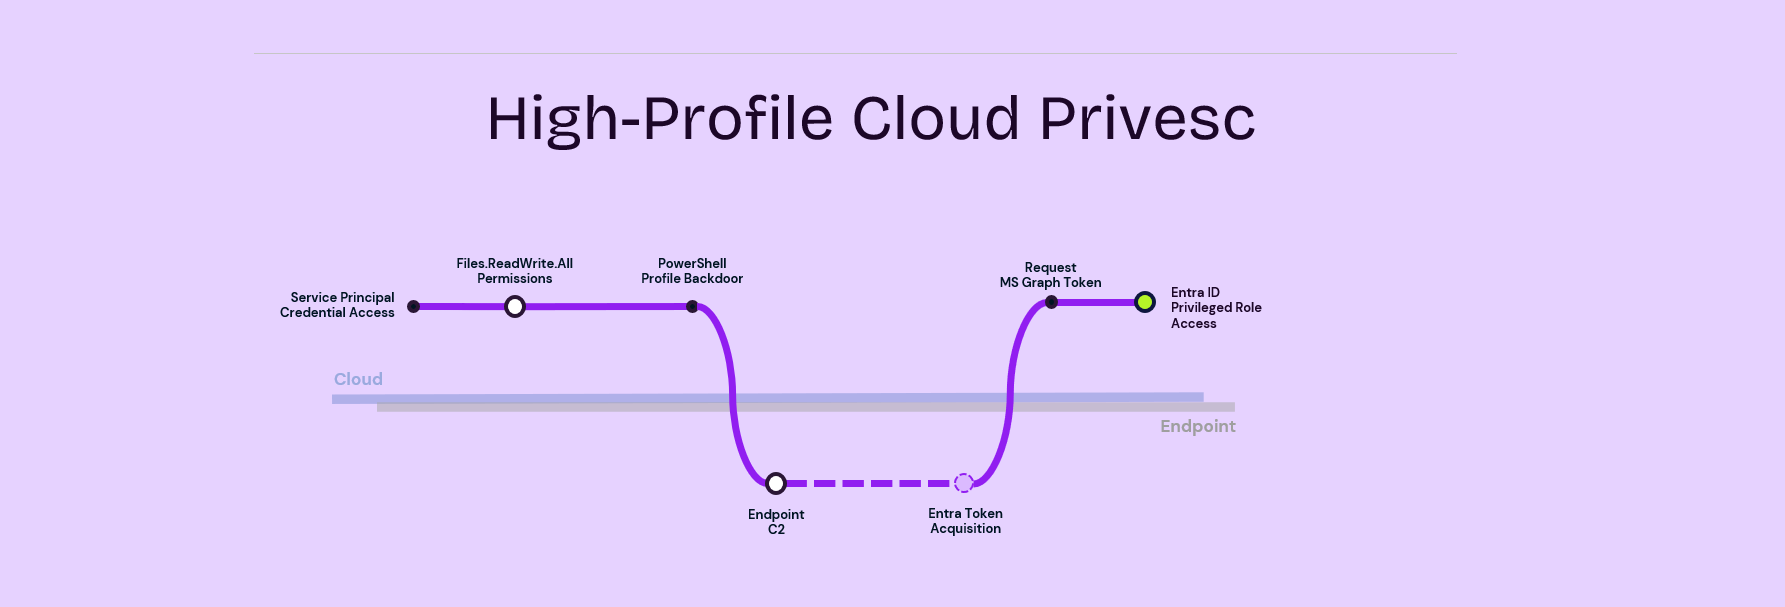 Revisiting PowerShell Profile Tricks in Entra Environments
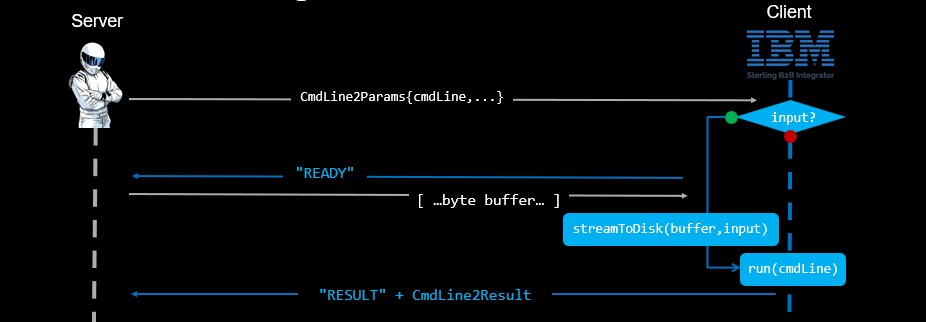 Older versions of the IBM Sterling B2B Integrator solution were affected by an exploitable RCE vulnerability (CVE-2024-31903) and a command injection weakness if authentication was disabled.
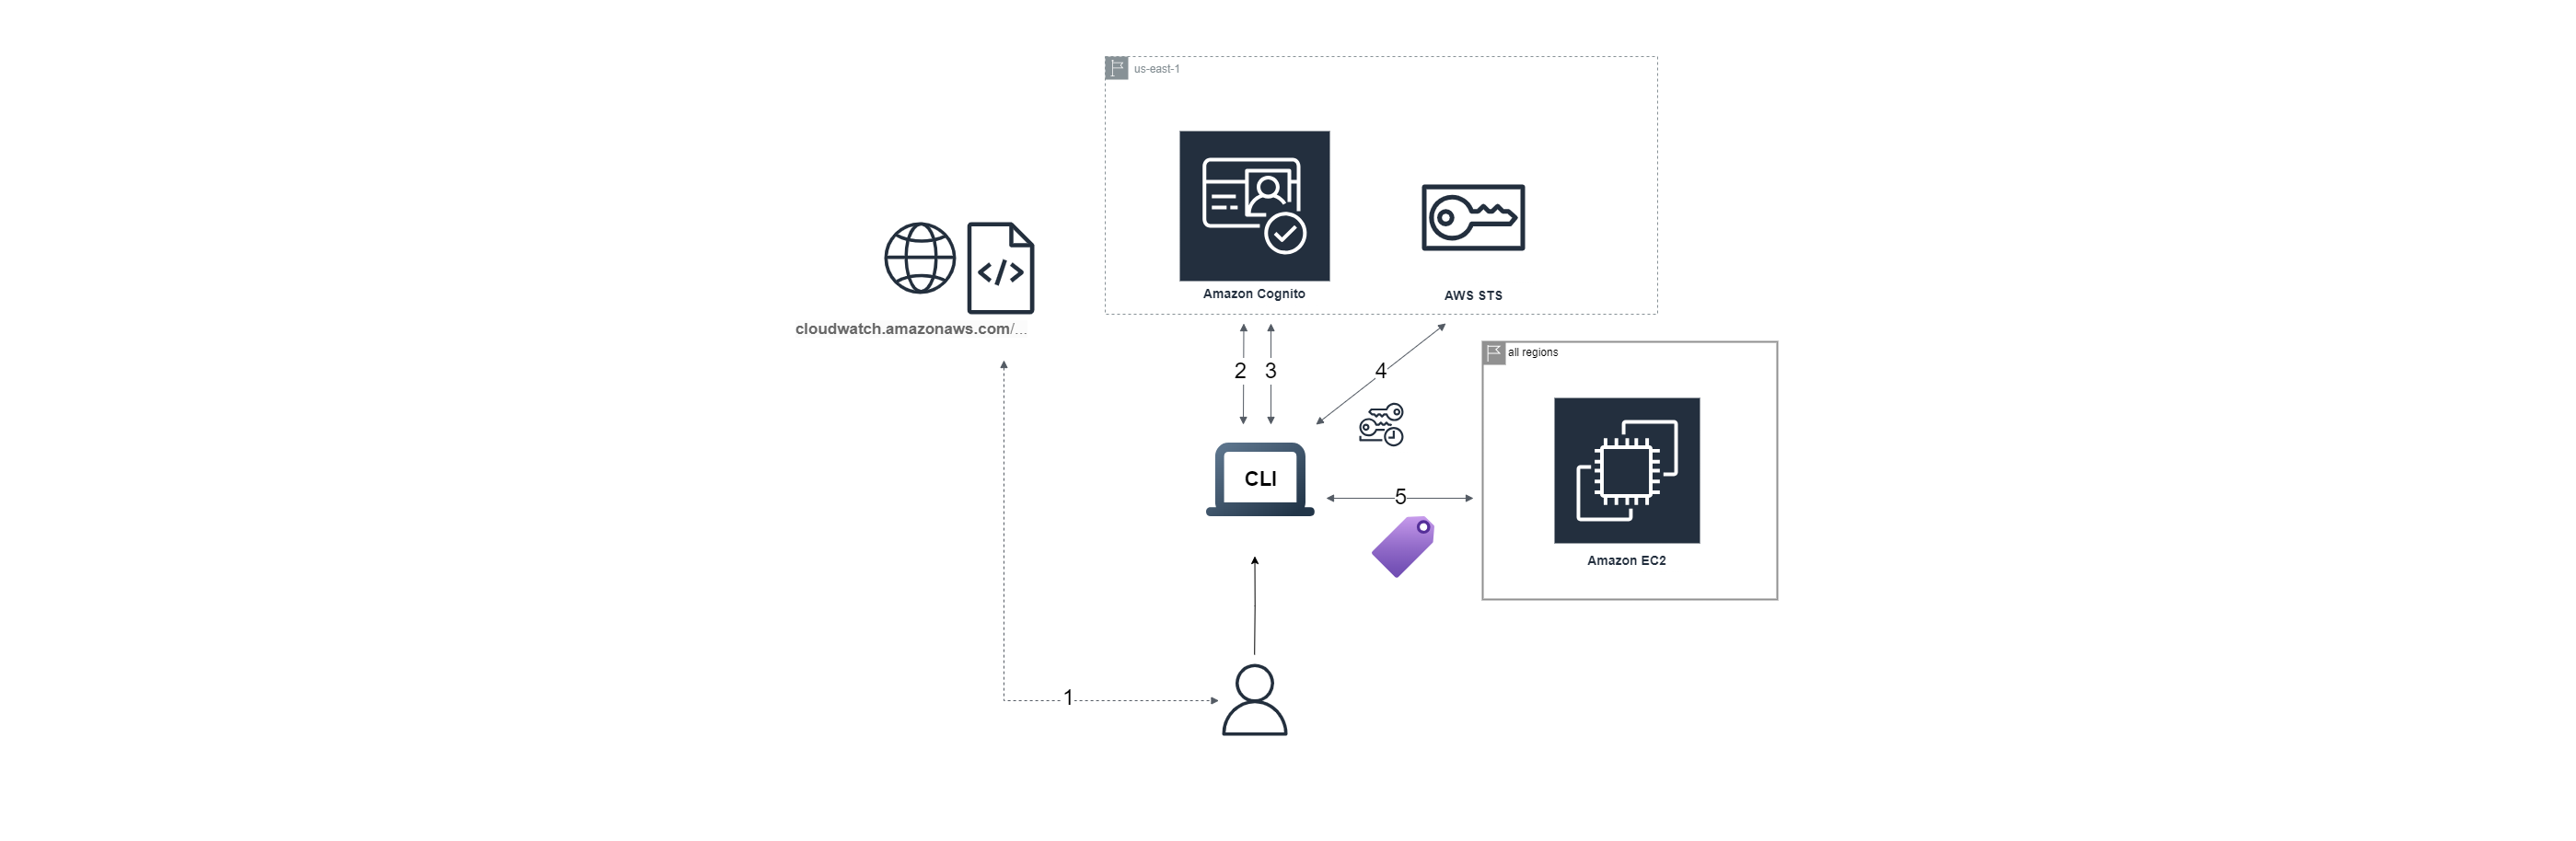 A security vulnerability in AWS CloudWatch dashboard sharing allowed unauthorized viewers to access EC2 tags.
 While scrolling my timeline on some social medium one day quite some time ago, I bumped into a post by (then) Offensive Security advertising a new version of Kali called 'Kali Purple'. I watched the linked video and realised it was actually a plug for their new course, 'SOC-200' targeting... blue teamers! OffSec doing DefSec?, I thought, that would be interesting...